PATH A
The bare API loop
alina-loopd calls the model directly. Four client tools, a token budget, and credentials that stay outside the model’s shell.
- Loop owner
- alina-loopd
- Billing
- API usage, with a budget cap
- Tested with
- A scripted model endpoint
Keep the loop.
Give everything else a better home.
Unharnessed is an agent-native operating system research prototype built on NixOS. Let the model reason. Let the OS own the permissions, the audit, and the undo.
Explore the architecture Read the thesis“No harness” doesn’t mean no structure.
It means putting structure where it belongs.
The irreducible part of an agent harness is a loop: call the model, run an action, return the result, and stop. The rest—memory, permissions, scheduling, secrets, recovery—already has a natural home in an operating system.
Unharnessed explores that boundary. A small loop and four primitives sit on top of NixOS. The model chooses what to do. The OS decides what it can touch.
For coding, lightweight scaffolding already goes a long way. General desktop work is less settled. That’s why this design prefers structured state and accessibility trees, with pixels as a fallback.
Models are brains.
Harnesses are hands.
The OS owns the self.
Every tool call crosses the same boundary.
Every action leaves a record.
Run a shell command as the agent’s dedicated Unix user, inside bubblewrap. A writable workspace. A read-only system. No host secrets and no network inside the shell sandbox.
The shell is subject to the rules—not an escape hatch around them.
intent  → sh
command → ls /work
scope   → sandbox
result  → workspace files
ledger  → recorded
A desktop that doesn’t fight you for focus. The agent operates its own headless compositor, under a separate user. A watch-and-take-over VNC view is planned for hardware.
| Responsibility | Its OS-side home | Prototype status |
|---|---|---|
| Permissions | Unix user · bubblewrap · nftables | VM tested |
| Audit | Intent + result ledger | VM tested |
| Undo | NixOS test activation + health probe | VM tested |
| Secrets | systemd credentials · isolated runtime login | VM tested |
| Resource limits | systemd slice · token budget · turn limit | Implemented |
| Memory & continuity | Loom + ai-memory context reconstruction | Planned |
| Scheduling & wakeups | systemd timers + desktop events | Integration planned |
The backend changes who runs the loop.
It doesn’t change what the model can touch.
alina-loopd calls the model directly. Four client tools, a token budget, and credentials that stay outside the model’s shell.
Keep the vendor’s compaction and session handling. Disable native tools. Expose the same four primitives through alina-mcp.
Claude Code adapter implemented; live-model validation is still ahead. Codex via its app-server is planned. Each runtime gets its own isolated login and configuration.
A gate the shell can walk around
isn’t a gate.
The dedicated user, private desktop, sandbox mounts, egress rules and resource caps apply outside the model’s reasoning. Secrets stay with the loop. Messages to people go into an approval queue.
Intent is logged before execution; the result is logged after. If the ledger can’t be written, mutating actions are refused.
The agent names a proposal, never an arbitrary path for root to run.
A privileged broker resolves the candidate, activates it temporarily, and probes its health.
A failed probe restores the prior system. A successful test stays active until reboot.
Durable changes are intended to flow through the Nix flake. The prototype uses pre-built candidates; building from commits and promoting a system to the boot default are not built yet.
The prototype exercises the tool boundary, desktop interaction, credentials, outbound queue and rollback in a two-VM NixOS test.
These results are from the author’s prototype report, not an independent audit or a live-model benchmark. They don’t establish complete isolation under every workload.
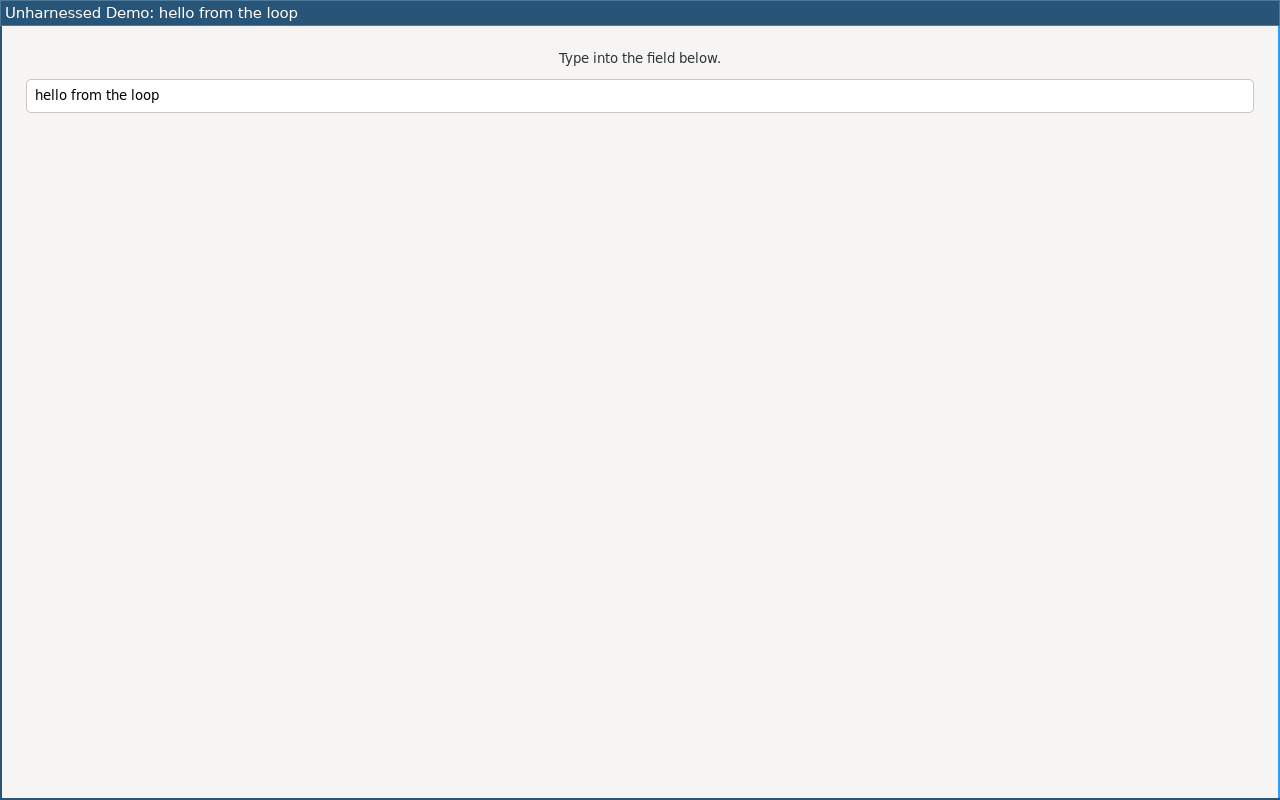
act, observed by see.Scripted model calls carried the credential, adaptive thinking, fallback configuration and exactly the four tool definitions.
Typed text was recovered in the window title, the accessibility tree and a screenshot.
Tests found no access to the operator’s seat, credentials, input device, ledger or network. Process-memory and cross-process root-path probes were denied.
The agent user could reach the allowed model endpoint, but not the outside server or the operator’s seat. The egress rule did not constrain root.
The test credential did not appear in tool output or transcripts and was supplied at runtime, not stored in the Nix store.
A failing candidate was rolled back. A healthy candidate stayed active, and the agent loop continued running.
An email request remained pending. Nothing reached the outside server. A dispatcher for approved items is still planned.
A stand-in Claude CLI used real MCP calls with only the four tools exposed. Its login was readable by the runtime but inaccessible to the model’s shell, including through process root paths.
Every exercised tool call had an intent entry and a result entry. All four primitives appeared in the ledger.
Unharnessed is an independent research prototype.
Not a production release. No install required to explore the idea.